A widely used browser extension, Twitch Enhanced Viewer | JeetBot, has been caught transmitting sensitive OAuth session tokens to a third-party commercial service. With over 30,000 installs, the breach poses a massive privacy risk to Twitch users.
- The 'Twitch Enhanced Viewer | JeetBot' extension is leaking user OAuth tokens to external servers.
- Over 30,000 users have installed this malicious or compromised tool via Chrome and Firefox stores.
- Data is being routed through JeetBot, a Russian-language commercial bot service.
- Security experts urge immediate removal of the extension and session reset.
A major security vulnerability has been uncovered involving a browser extension named Twitch Enhanced Viewer | JeetBot. Available on both the official Chrome and Firefox web stores, the extension has been identified as transmitting users' Twitch OAuth session tokens to a commercial bot service, potentially granting unauthorized access to user accounts.
Marketed as a legitimate utility to block ads, force 1080p playback, and bypass regional restrictions, the extension has amassed more than 30,000 installs. However, an investigation by application security firm Socket reveals a much more sinister underlying mechanism designed to capture authorization headers and extract user credentials.
Why This Matters
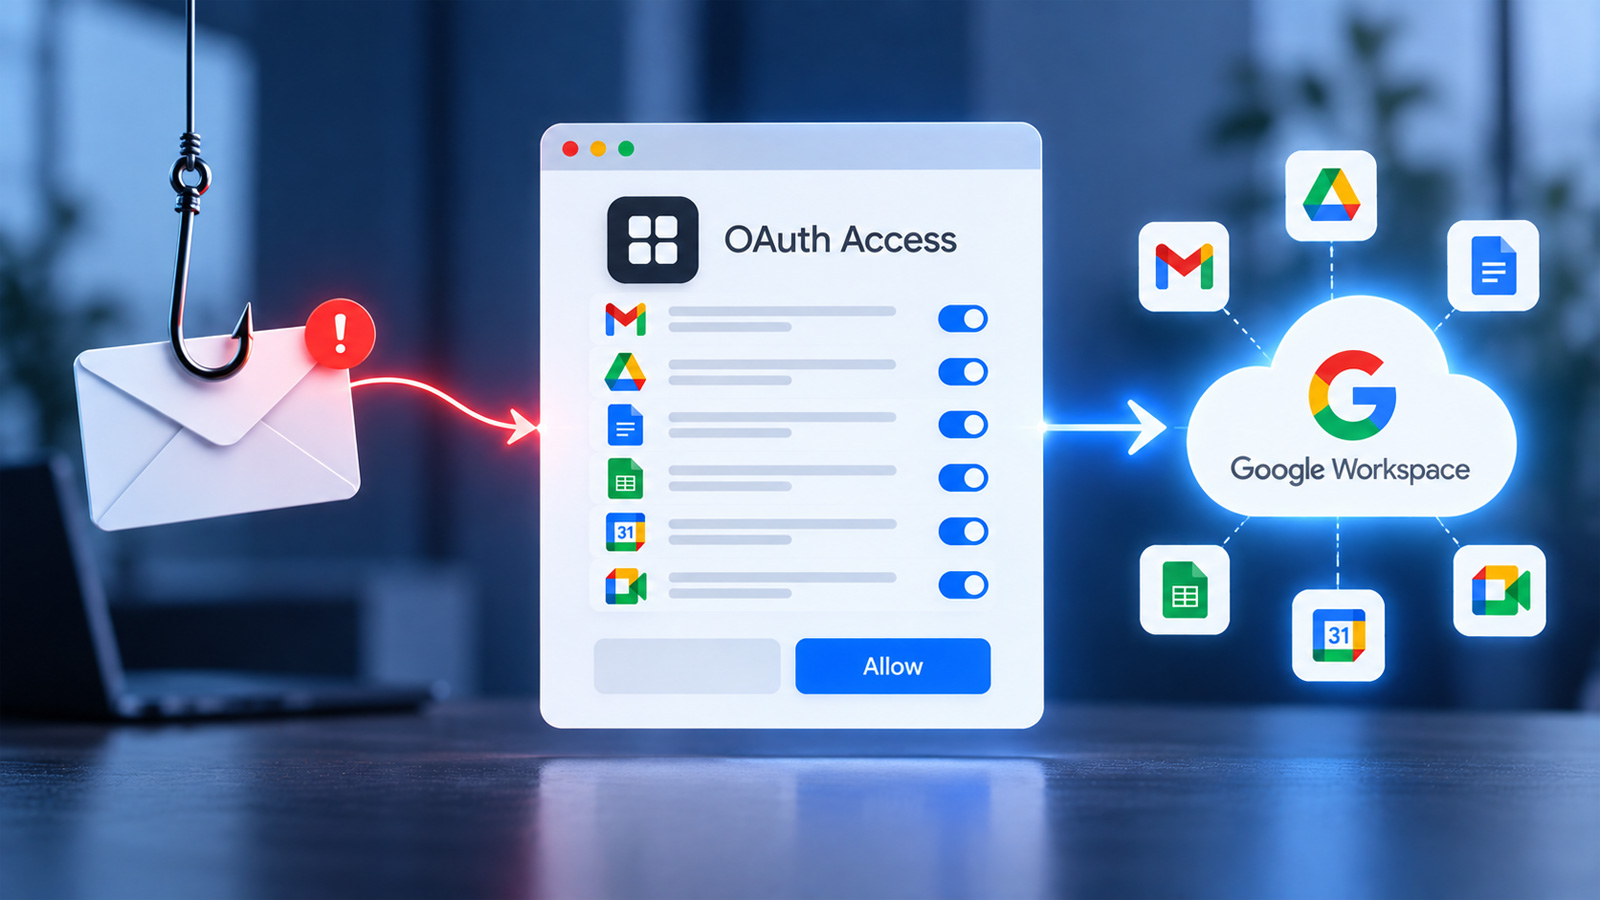
BozokMedia analysis shows that the exposure of OAuth tokens is far more dangerous than a simple password leak. An OAuth token acts as a digital passkey; if intercepted, an attacker can impersonate the user and bypass multi-factor authentication (MFA) to access private data, settings, and streaming controls without ever needing the actual password.
When authentication tokens are passed in cleartext via URL parameters, the entire security architecture of the platform is effectively bypassed.
The technical execution involves the extension redirecting Twitch’s video playlist requests through a proxy server. During this redirection, the extension appends the user's token as an &auth= query parameter. Because the token resides within the URL string, it is recorded in plain text within the proxy server's request logs, making it easily retrievable by the developers of JeetBot, a Russian-language service.
| Feature | Advertised Function | Actual Malicious Activity |
|---|---|---|
| Video Quality | Force 1080p/1440p | Data Exfiltration via Proxy |
| Ad Blocking | Remove Interruptions | Intercepting Auth Headers |
| User Privacy | Claims 'No Data Collection' | Sends Tokens to JeetBot Logs |
Historical Background
The history of browser extensions is riddled with 'malvertising' and data-scraping incidents. From crypto-drainers to VPNs that track browsing history, malicious developers frequently leverage the trust users place in official app stores to deploy spyware that operates under the guise of helpful productivity tools.
Frequently Asked Questions (FAQs)
1. What should I do if I have this extension installed?
Immediately remove the extension from your browser, log out of all active Twitch sessions, and re-authenticate to invalidate any stolen tokens.
2. Is my password also stolen?
While the extension focuses on the OAuth token, it is highly recommended to change your password as a standard security precaution.